

When people hear the “phrase encrypted video conferencing,” it is meant to create confidence. It tells us that our conversations are protected as they move between people, devices, and locations.
Encryption provides that protection, but the security of a video meeting also depends on who manages the infrastructure, what metadata is stored, and how access is controlled. For organizations handling sensitive conversations, understanding these additional layers is an important part of evaluating video conferencing security.
Does end-to-end encryption protect video conferences?
End-to-end encryption (E2EE) can provide important privacy protection in publicly hosted video conferencing. In an E2EE meeting, media is encrypted and decrypted on participant devices, which limits the platform provider’s ability to access meeting content.
However, even when E2EE is in place, organizations still rely on the platform’s identity systems, software implementation, operational security practices, and metadata handling. Depending on the platform, enabling E2EE can also limit features that require server-side processing, such as recording, transcription, live captions, interoperability, and certain compliance workflows.
For healthcare, government, justice, defense, or other regulated sectors, that trade-off matters. These teams often need strong privacy protections, but they may also need auditability, accessibility, compliance workflows, and the ability to connect across different systems.
In these cases, E2EE is an important security feature, but it does not address every aspect of video conferencing security. Metadata is one example of information that can remain visible even when meeting content is encrypted.
What does video conferencing metadata reveal?
Even when meeting content is encrypted, metadata often remains visible to the platform operating the service.
That metadata may include:
- Who joined a meeting
- When it took place
- How long it lasted
- Which devices or locations were involved
In some environments, that information can itself become sensitive. A healthcare appointment may expose a patient relationship. A legal hearing can reveal case activity. Operational meeting patterns may expose information even when the meeting content itself remains protected.
Read our complete guide to video conferencing encryption here.
What makes video conferencing secure beyond encryption?
Organizations handling sensitive communication typically evaluate several layers of security together:
- Encryption protects meeting content in transit.
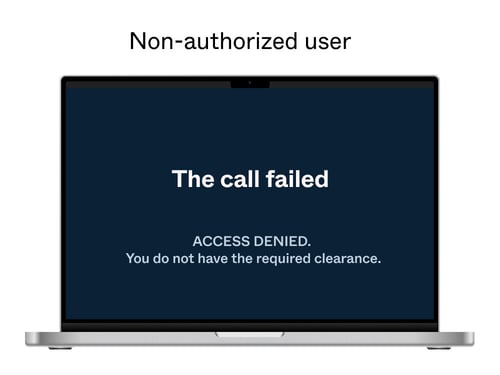
- Authentication helps verify identities before access is granted.
- Access controls determine who can join, present, or share information.
- Deployment architecture affects who operates the infrastructure and where data is processed.
There is also an element of operational governance. Organizations often need visibility into logging, auditability, retention policies, and compliance controls, especially when video is part of regulated workflows.
This is where identity management, zero trust architectures, and data sovereignty need to be considered when evaluating secure video collaboration solutions.
Why does the deployment model matter for secure video conferencing?
The way a video platform is deployed shapes how much control an organization has over the broader meeting environment.
In publicly hosted platforms, the provider typically manages the infrastructure, operational policies, and surrounding cloud environment. That model works well for many organizations and collaboration scenarios.
Other organizations require tighter operational control, particularly in sectors like healthcare, government, justice, defense, and critical infrastructure. That may involve self-hosted deployments, private cloud environments, or infrastructure designed to meet specific sovereignty, compliance, or security requirements.
With a self-hosted deployment, organizations can keep critical communications within their own operational and regulatory boundaries. Because the infrastructure stays under their control, the trust boundary stays there too.
How does Pexip support secure video conferencing?
Pexip gives organizations control over where and how their video meetings run, with deployment options including on-premises, private cloud, and highly controlled environments.
Pexip combines encryption with authentication, access controls, and flexible deployment architecture, giving organizations the ability to protect meeting content while maintaining control over the wider meeting environment.
For organizations handling sensitive or regulated communications, that means they can choose where data is processed, how access is controlled, and who operates the infrastructure supporting their meetings.
Explore Pexip’s secure, self-hosted video conferencing solutions.
Originally published: October 10 2023
- Secure collaboration
- Secure Meetings